- Roles and permissions
- Ten role templates, custom roles, four levels per module and project-level access. Enforced on the server for every request.
- Tenant isolation
- Three layers: organisation-scoped queries, a tenant-bound data client and row-level security in PostgreSQL.
- Audit log
- Who changed, approved or exported what and when – stored immutably, filterable and exportable as CSV.
- GDPR-oriented structure
- Organisation data export, per-person disclosure, anonymisation, data minimisation for incidents. AI services only after explicit approval.
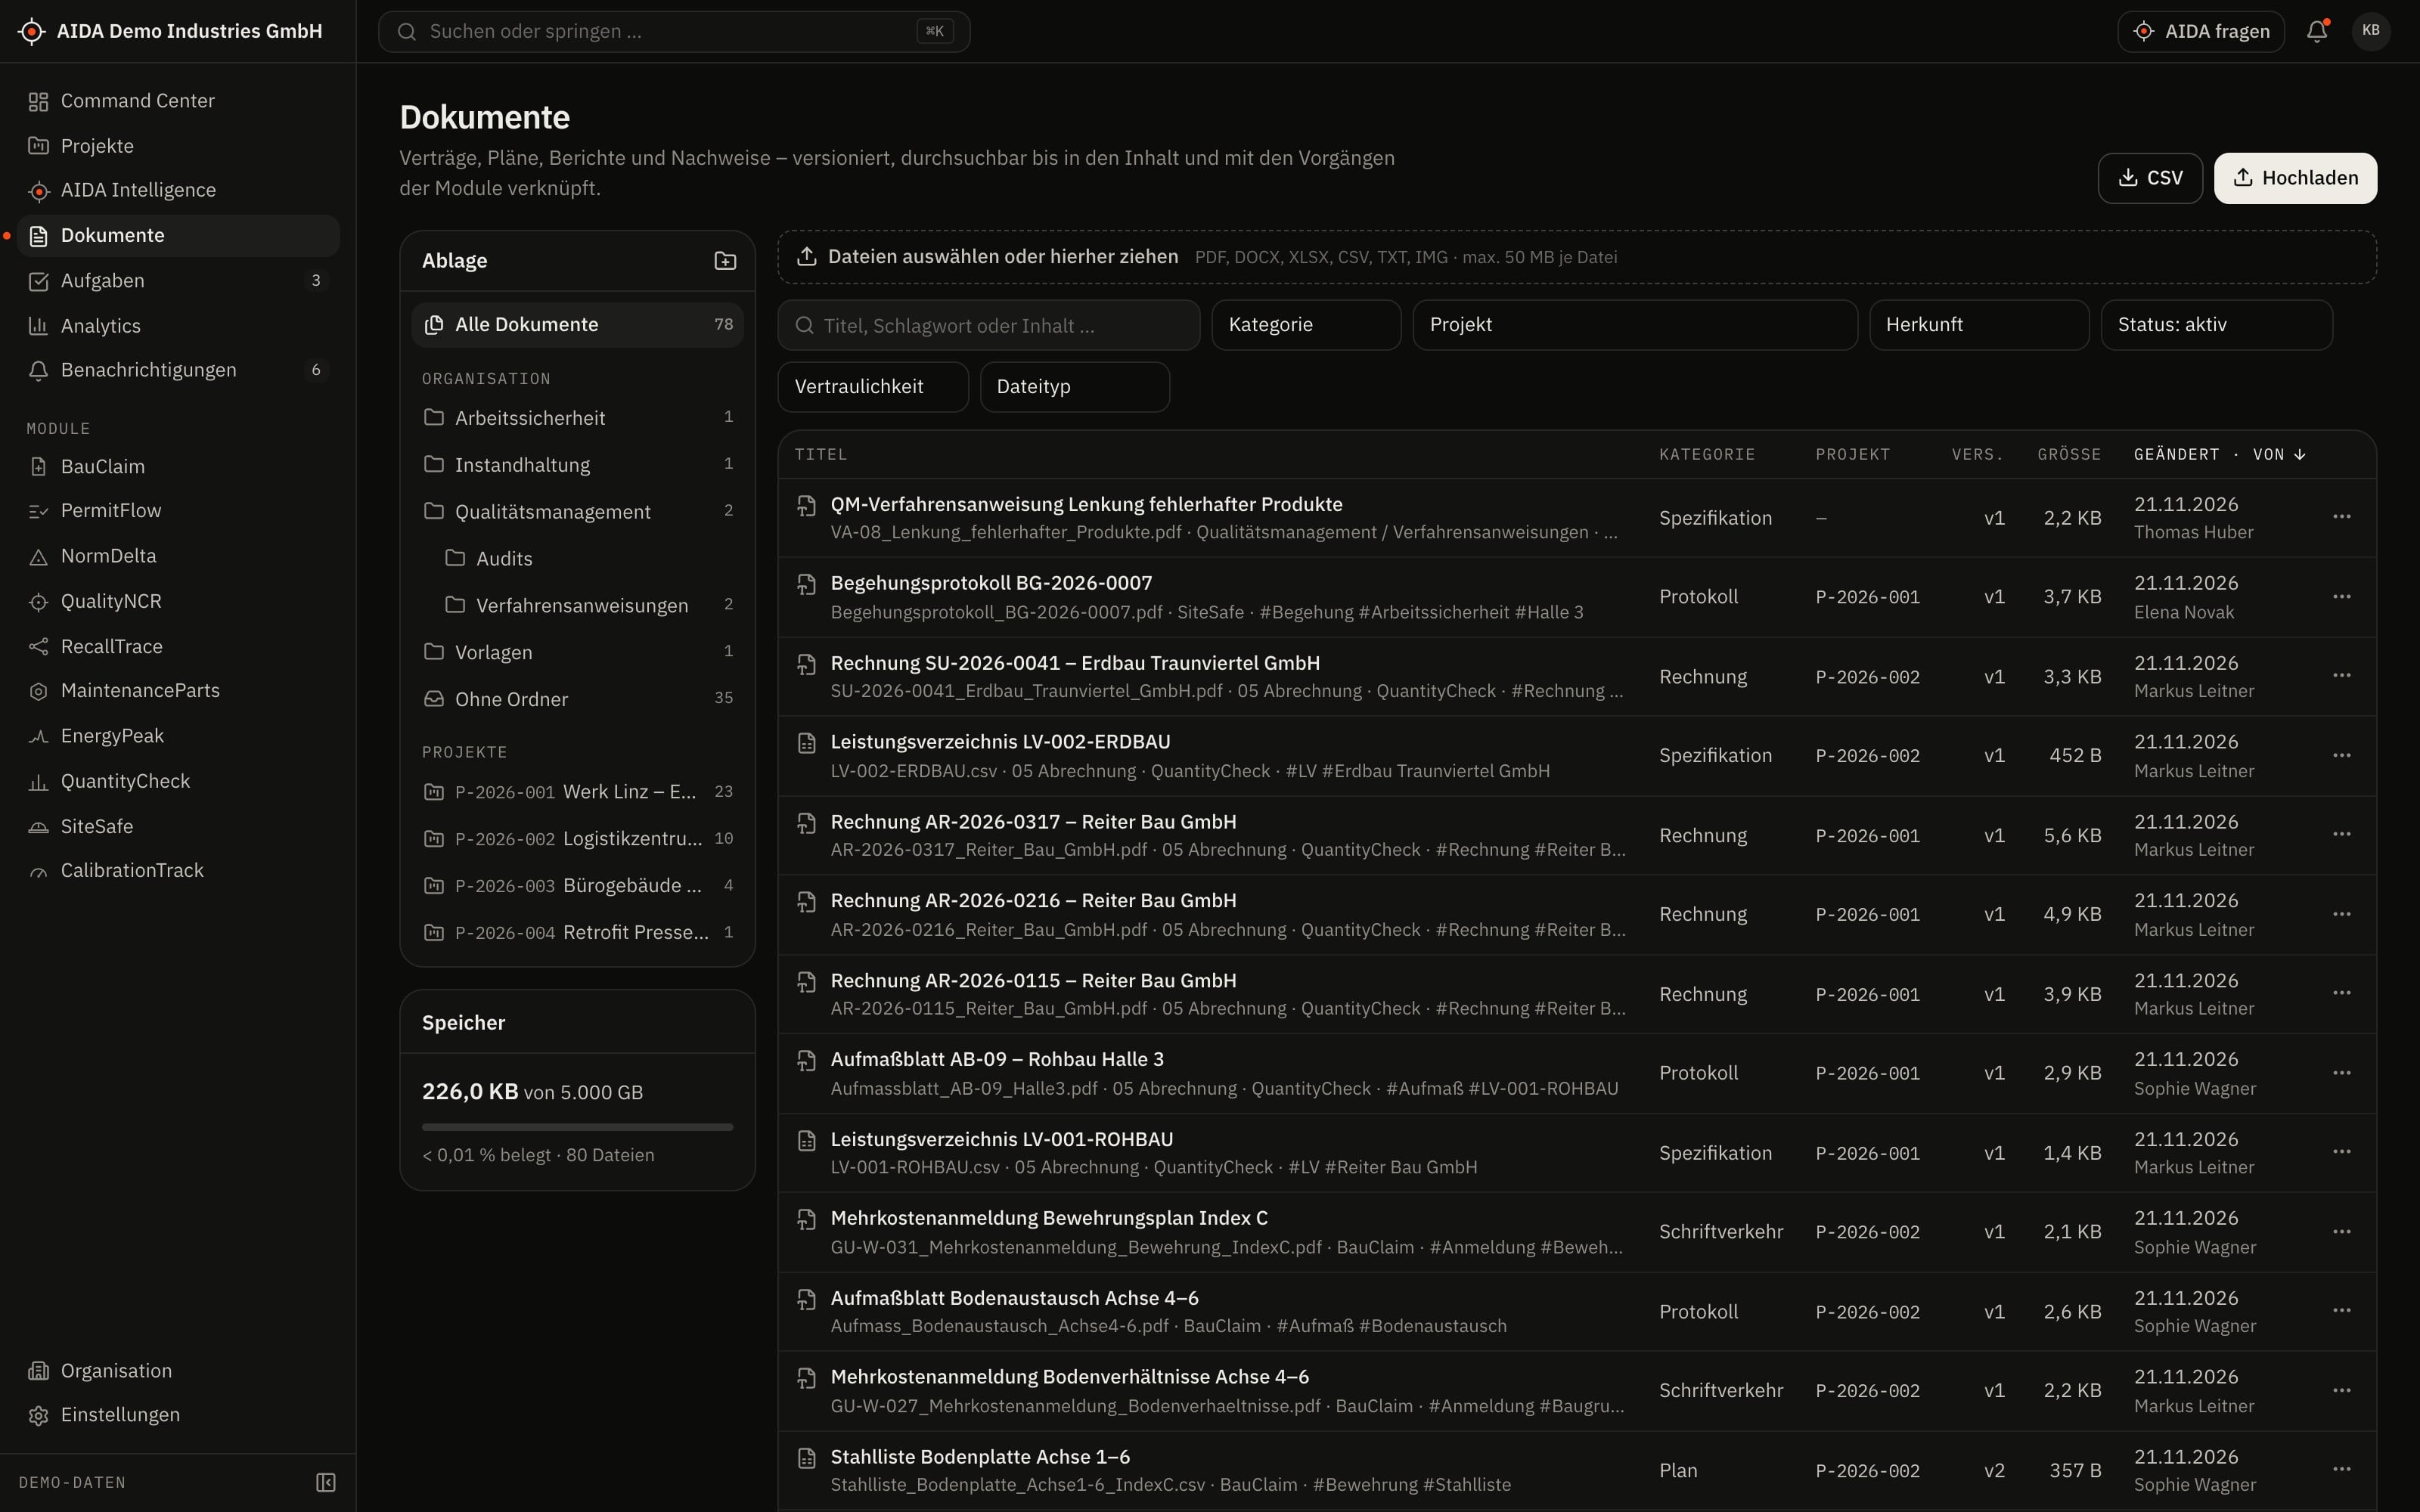
- Document storage
- Versions with checksums, confidentiality levels, file-type validation, full-text search. Local or S3-compatible storage.
- Export and interfaces
- CSV, PDF and ZIP exports in every module, import from CSV and XLSX, REST API with API keys.
- Prepared for EU hosting
- Container deployment, PostgreSQL, S3-compatible storage. Where AIDA runs is agreed with the operator.
- Sign-in
- Two-factor sign-in (TOTP), session management, lockout after failed attempts. SSO via SAML/OIDC is in preparation.